Write Permissions Setup: Separate vs Shared
Overview
Write permissions are additive. Your Azure cloud account still needs the baseline read permissions from Azure Cloud Account Setup. Reservations Contributor stays optional and is only needed for reservation refund quotes and reservation management.
Credential Configuration Options
Write-back can reuse the read app or use its own app registration. Separate credentials are recommended for production.
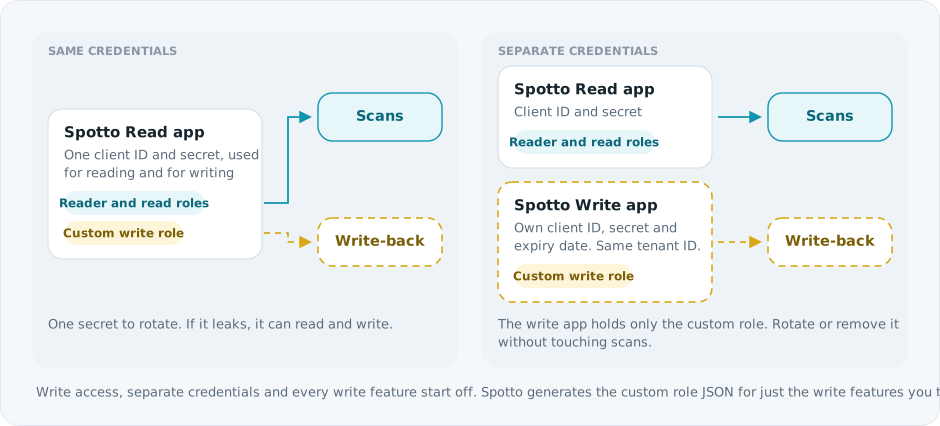
With separate credentials, keep tenant-wide governance, reservation provider and Microsoft Graph permissions on the read app. Give the write app only the Azure RBAC actions for the write features you enable.
Steps to Enable Write Permissions
- Go to Connectors -> Cloud Accounts in the Spotto Portal.
- Select your Azure cloud account or create a new one, and configure the read access credentials if needed.
- In Write Permissions Configuration, turn on Enable write access.
- For separate credentials, also turn on Use separate credentials for write operations and enter the Write Access Client ID, Write Access Client Secret Value and Secret Expiration Date. The tenant ID is shared with the read credentials.
- Under Write Permissions, tick the features you want:
- Dismiss Azure Advisor Recommendations
- Enable Storage Inventory Reports (inventory analysis is reader-only today; see Storage Inventory)
- Create Azure Policy Exemptions (see Policy Exemptions for the management-group role)
- Expand Custom Role for Least Privilege, copy the JSON, and create and assign the role in Azure. See Custom Roles.
- Select Validate Connection, then Update to save.
Validate Connection signs in with the write credential and reports how many subscriptions it can see. It does not check the custom role's actions. Azure checks those when Spotto first acts, for example when you dismiss a recommendation.
Turning off Enable write access and saving removes the stored write client ID, secret and expiry date. You need to enter them again to turn write access back on.
Create a Separate Write App
1. Create an Entra ID Application
- Go to the Azure Portal and sign in.
- Open Microsoft Entra ID > Manage > App registrations > New registration.
- Enter a name, e.g.
Spotto Write. - Under Supported account types, choose Accounts in this organizational directory only.
- Leave the Redirect URI blank, then select Register.
Record the Application (client) ID and Directory (tenant) ID.
2. Create a Client Secret
- In the app registration, go to Manage > Certificates & secrets.
- Under Client secrets, select New client secret.
- Enter a description (e.g.
SpottoWriteSecret) and choose an expiry period (recommended: 12 months). - Select Add.
Copy the Client Secret Value immediately. It won't be shown again. Also record its expiry date.
3. Assign Required Roles
Assign the custom role for the features you ticked to the write app:
- Dismiss Azure Advisor Recommendations: create and assign the custom role
- Create Azure Policy Exemptions: Policy Exemptions
- Enable Storage Inventory Reports: Storage Inventory access model
If validation or a write action fails, see Troubleshooting. For rotation and revocation, see Security Best Practices.
For further assistance, please Contact Us.